Security Audits, Prepare Your Firm to Meet Your Current and Potential Client Requirements
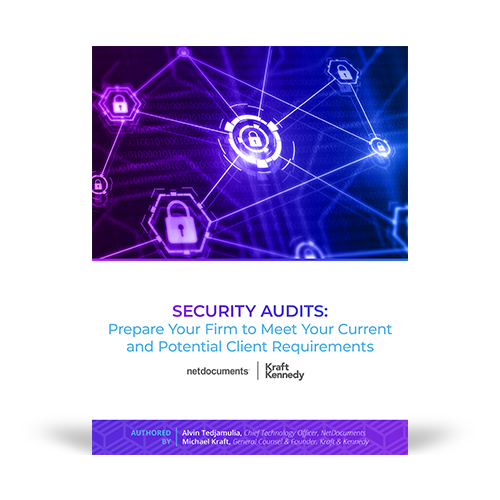
Get Peace of Mind Knowing Your Data is Secure
Now, more than ever, law firms are expected to effectively safeguard their documents against ever-evolving threats.
Recent high-profile data breaches at global and smaller firms have led your current and potential clients to increase scrutiny of their outside counsels’ cybersecurity. International banks, major corporations, and government agencies are focused on vetting the internal controls and security practices of legal document systems and requiring extensive disclosures on compliance and information governance practices.
Download this article to get access to insight from Alvin Tedjamulia, CTO and co-founder of NetDocuments, and Michael Kraft, founder and CEO of Kraft Kennedy, as they dissect key security requirements that your potential and current clients are requiring in a security audit including:
- Encryption requirements
- Datacenter best practices that address questions often raised in RFPs and audits by clients
- End-user protection and technologies that improve the safeguarding data from the back end and front-end
- Certifications that your Cloud DMS provider should have to ensure maximum value
Access this content
More resources for you
-
- Webinar
Is Your Tech Stack Built for the Business or Practice of Law? (Part 1)
In this 40-minute webinar, learn the difference between software that runs…
-
- Webinar
Context Matters: What It Takes to Turn Legal AI Spend Into Impact
Is your firm’s foundation helping AI deliver – or holding it…
-
- eBook/Whitepaper
The Context Advantage for Firms Using a Practice Management System (International Edition)
Your practice management system knows what happened. It doesn’t govern what…
-
- eBook/Whitepaper
The Context Advantage for Firms Using a Practice Management System (US Edition)
Your practice management system knows what happened. It doesn’t govern what…